Most lists of security awareness topics look alike. They give you ten topics, or twenty-five, or fifty, and none of them helps you decide which ones matter for your organization. Choosing is the part you actually have to do.
A list is a starting point. This page groups topics by the attack surface they defend, flags the ones that are new for 2026 and missing from most syllabuses, and covers how to choose an order instead of training everything at once. Think of it as a working guide to security awareness training topics for the year ahead.
How to choose which security awareness topics to cover
Any list of topics is easy to produce. Deciding which few to run this quarter takes judgment, and the best input is attack data: what's hitting your industry, what your last simulations exposed, and which roles hold the access an attacker wants.
Industry reports on current cybersecurity threats are a good place to start. If you train phishing hardest because it's the best-known topic, while your help desk has never faced a reset-request test, you're working from a catalog.
Eight to twelve core topics, taught in short bursts all year, will do more than fifty covered once. Short quizzes after each burst show what people actually retained. The annual mega-module has two problems.
People forget it faster the longer it runs, and because everything arrives at once, you can't tell which parts landed. Spread across the year, cybersecurity awareness training also gives you a clearer read on which topics stuck.
A topic fades after one pass, so the syllabus rotates. For the decay curve behind that, read how quickly a topic fades once trained. For picking what comes next, letting your own threat data choose the topic works better than choosing from a list like this one.
Core security awareness topics every employee needs
These six apply to everyone, whatever their role. Each comes down to something a person does or doesn't do on an ordinary workday, and cyberattacks tend to exploit exactly those moments.
1. Phishing and email-based social engineering
Phishing runs from mass campaigns to spear phishing built on public research about the recipient, and the malicious link or credential-harvesting page is just the delivery. What follows a successful click can range from stolen logins to ransomware.
Pause on any message that creates urgency, check it before acting, and report it. A deleted message tells your security team nothing. That habit blunts phishing attacks even when a message gets past the filter, and staff should be able to spot malicious links before clicking.
2. Business email compromise and invoice fraud
In business email compromise, an attacker poses as an executive or a supplier to redirect a payment. No link. No malware. Nothing for a filter to catch, only a request that looks routine and arrives at a busy moment.
The habit that stops it is verifying any change to payment details through a number already on file, never one supplied in the message.
3. Passwords and multi-factor authentication
Reused passwords, weak passwords, and accounts protected by a single factor give attackers an easy way in. Password security is mostly a matter of habit. Training should focus on using a unique password for every account through a password manager, turning on MFA when it's offered, and never entering credentials after an unsolicited prompt.
4. Data handling and classification
Regulated and confidential data leaves approved systems through personal cloud storage, unmanaged devices, and shared links left public. Employees need to know which category a piece of data falls into and keep it in the systems approved for that category.
The General Data Protection Regulation (GDPR), HIPAA, PCI DSS, and CCPA make this a compliance obligation as well as a security one. Data protection and data privacy obligations both depend on that daily habit. A policy document doesn't create it.
Training should cover careless leaks as well as insider threats, where someone misuses access on purpose. Personal phones and laptops brought in under a BYOD policy need particular attention, since they often sit outside managed device security and may lack antivirus software.
5. Physical security and clean desk
Tailgating through a controlled door, an unlocked screen, a document left on the printer, and a laptop taken from a desk all take no technical skill. Tailgating in particular defeats access control for anyone willing to follow someone in.
Staff should challenge or report anyone who follows them in without a badge, lock the screen every time they step away, and give a laptop left in a car the same care they'd give the data on it. Away from the office, they should also use the company VPN on public Wi-Fi.
6. Incident reporting
Incident reporting should come first, because it turns one person's mistake into detection for the whole organization. Employees who report early give your team detection that no filter provides. Human error can't be eliminated, so speed matters more than certainty.
The report has to go somewhere, and the reporter has to hear back. Phishing Triage gives people a one-click report button in the inbox and lets your team delete a malicious email across the organization.
Phishing simulations are a good way to practice this, since they let people use the report button before a real message arrives.
The 2026 security awareness topics most programs are missing
If your syllabus hasn't been rewritten in the last couple of years, check it against these five topics. Each one sits behind attacks and risks organizations are dealing with now, and many legacy libraries have little or nothing on them. They cover cyber threats that older syllabuses were not written to address.
1. Voice phishing and cloned audio
Attackers have moved to the phone, as shown by the incidents that landed this year. Verizon's 2026 Data Breach Investigations Report found that mobile-focused social engineering (fake texts and voice calls) was 40% more successful than email phishing. AI voice cloning makes a familiar voice cheap to fake, so a call that sounds like a manager or a vendor proves nothing about who is on the line.
Many legacy syllabuses leave this out, which is why it belongs on every 2026 list. Train people to verify identity through an independent channel before acting on any request made by phone, whatever voice is on the line.
2. Deepfake video and impersonation
The scenario to train is the approval request: a cloned executive on a video call asks for a payment, an exception, or an access change. Executives and their assistants should go first. They produce the public audio and video that cloning needs, and they hold the authority that makes the request worth faking.
People should confirm through a known channel before approving anything, even when the person asking is visible on screen.
3. QR code phishing
A printed code in a break room, a parking lot, or a conference pack reaches people email never touches. QR codes sit among the attack vectors that bypass the inbox entirely. Warehouse staff, drivers, clinical teams, and field engineers sit outside most awareness programs, and QR phishing (quishing) simulations are one of the few ways to reach them.
Teach everyone to treat a QR code like an unknown link and check where it leads before entering anything.
4. Safe use of generative AI at work
Employees paste customer records, source code, and contract terms into public AI tools because it saves time. You may have no policy covering this, or one nobody has read. Each paste is a data security risk, even when the intent is harmless. It's the topic where a new compliance obligation meets a new risk, and syllabuses have been slow to catch up with both.
The module should cover which tools are approved and which categories of data never go into any of them. Training employees on safe GenAI use covers what it needs to contain.
5. MFA fatigue and push-bombing
Teaching people to set up MFA and teaching them to defend it are separate jobs. An attacker with a stolen password can flood a user with push notifications until one gets approved just to stop the noise, and sometimes follows up with a call posing as IT and offering to help clear them.
Staff should know this happens, reject any prompt they didn't trigger, and report a flood of them as an incident.
Role-based security awareness topics
A flat topic list assumes every employee faces the same attacks. They don't, and the highest-risk roles need training the general population never will.
- Finance: business email compromise and payment verification, practiced until it's a reflex, since finance sits at the end of most fraud chains.
- Engineering: credential theft and supply-chain attacks.
- IT and help desk: reset-request social engineering, the method Scattered Spider (tracked by Mandiant as UNC3944) is known for.
- HR and recruiting: synthetic candidates and fake identities.
- Executives and their assistants: whaling and impersonation of the people they approve requests for.
Each role deserves its own path. Four reflexes your help desk agents need to practice shows what one of those paths looks like in practice.
Turning a topic list into training
Every page competing for this search ends at the list, and a list is not training. Someone still has to build a module on each topic, keep it current as threats change, and get it to the right people. That's where programs stall, because it's where the list meets a vendor's release schedule.
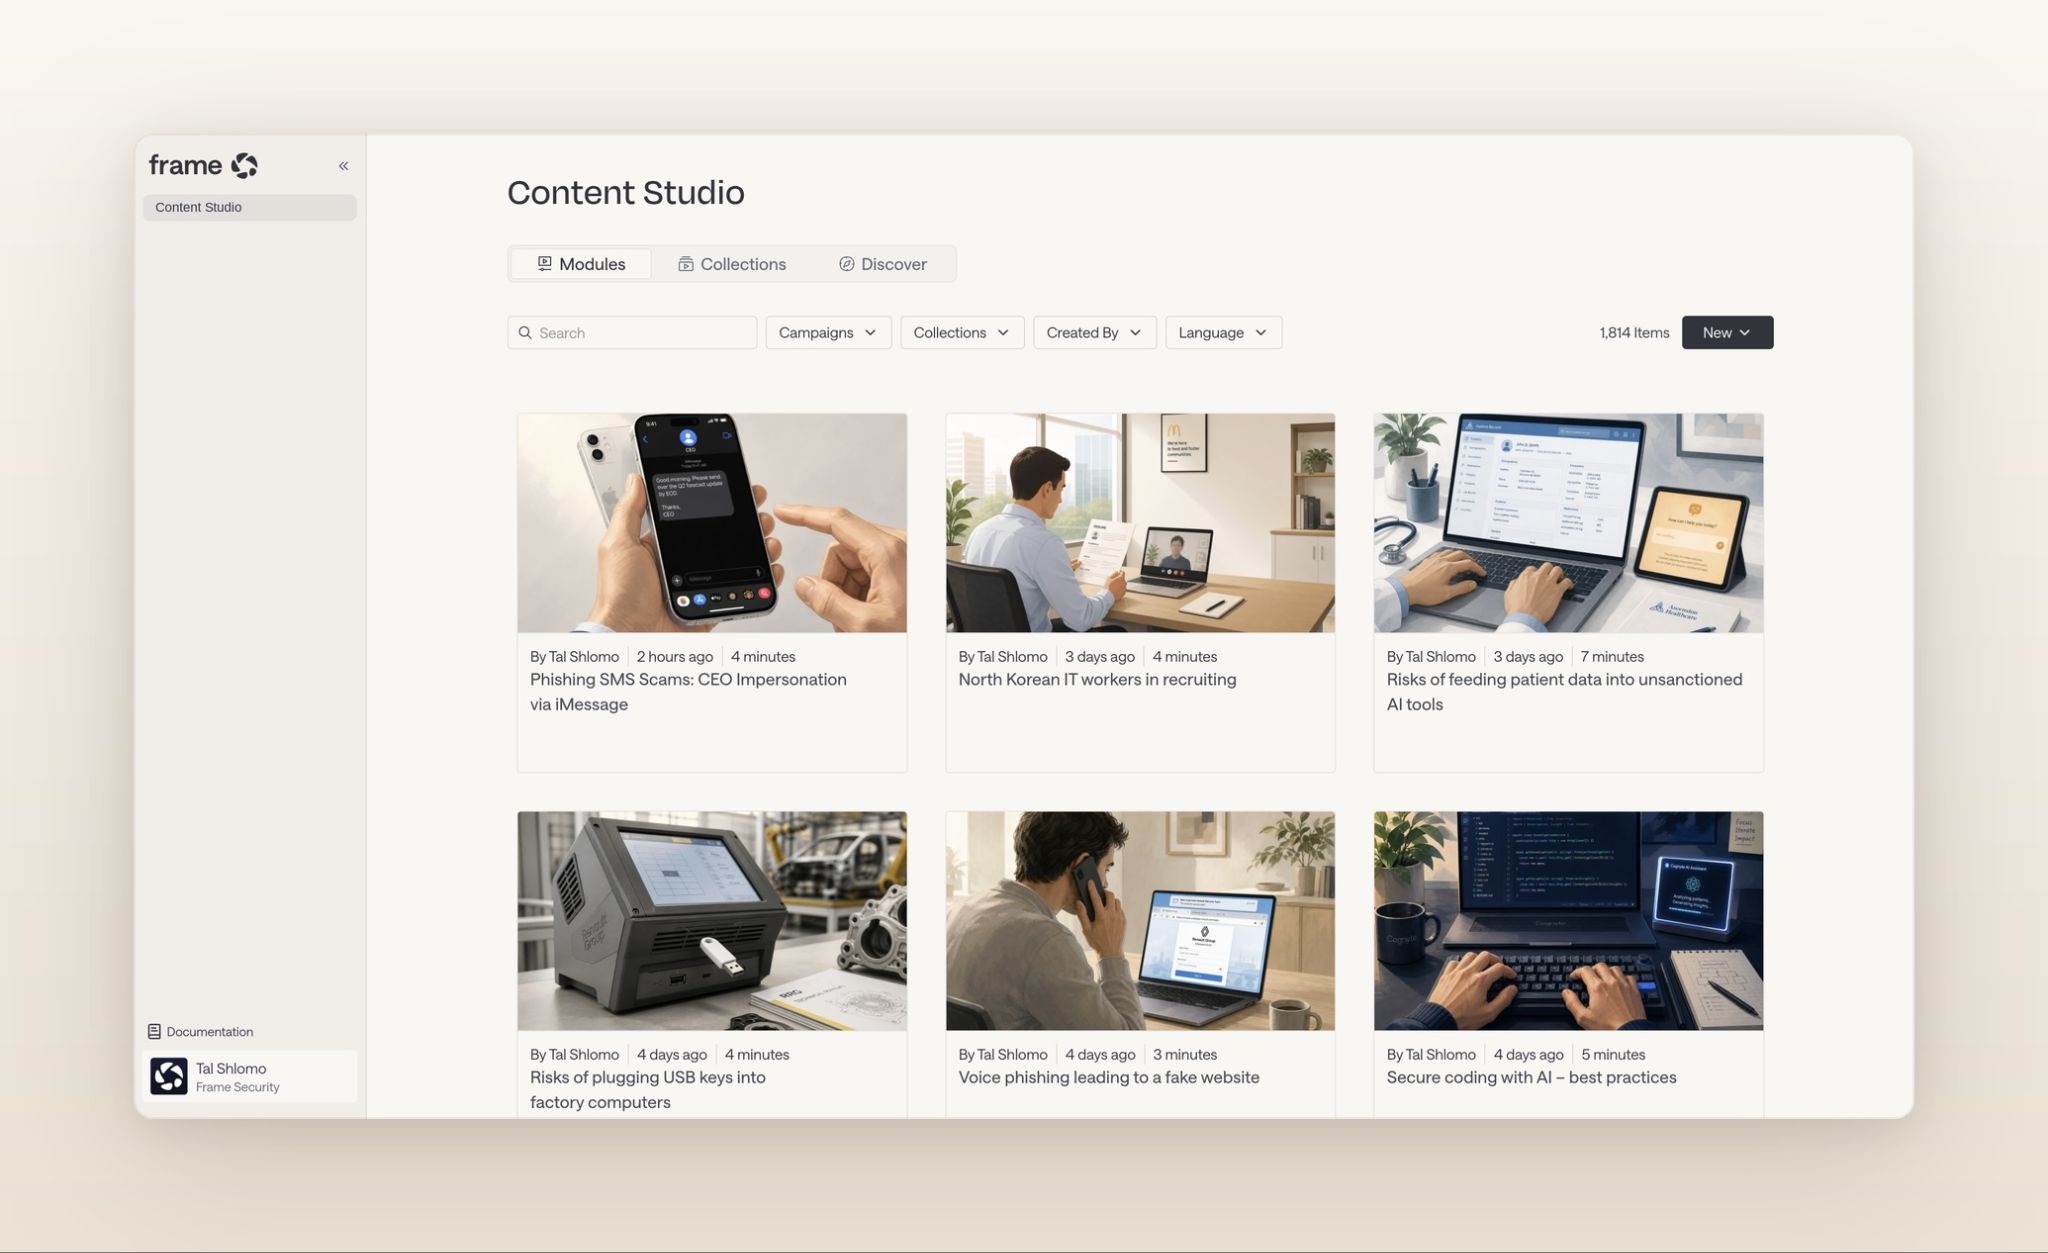
Frame Security is an AI-native Human Risk Security platform built for that gap. Its security awareness training includes AI Content Studio, which generates a module on any topic on this page from a short description.
AI Content Studio builds it around your policies and systems, produces it in more than 70 languages, and lets you edit it before you assign it. A topic you spot on Monday can be training this week, with no wait for a vendor to add it to a library.
North Korean IT worker schemes, tracked by Microsoft as Jasper Sleet and by CrowdStrike as Famous Chollima, make a good test case. If you hire remote engineers, you may already be interviewing these candidates, because operators use AI-generated identities to win the jobs.
Unit 42 gave the task to a researcher with no image-manipulation experience, who built a convincing real-time synthetic identity in 70 minutes using free tools and a five-year-old graphics card. Most syllabuses have no module for it. For your recruiting team, you describe the threat and review what Content Studio generates.
Discover handles the choosing step. It recommends the next topic from your organization's own threat and behavior data, which is the method the choosing section above describes, applied continuously.
Results from that training and from your phishing and deepfake simulations feed a per-employee Human Risk Score, which is how you track human risk reduction and see whether the topic changed anything. Tying training to measured behavior is what Human Risk Security means in practice.
The list is the easy part. What matters is how fast the topic that counts this month becomes training your team has completed. Book a demo and bring the topic your current library has no module for.
